Autonomous AI penetration testing
An engine and agentic orchestration framework that plans, executes and iterates on security tests through tool-driven workflows, with people reviewing rather than driving each step.
/ ABOUT
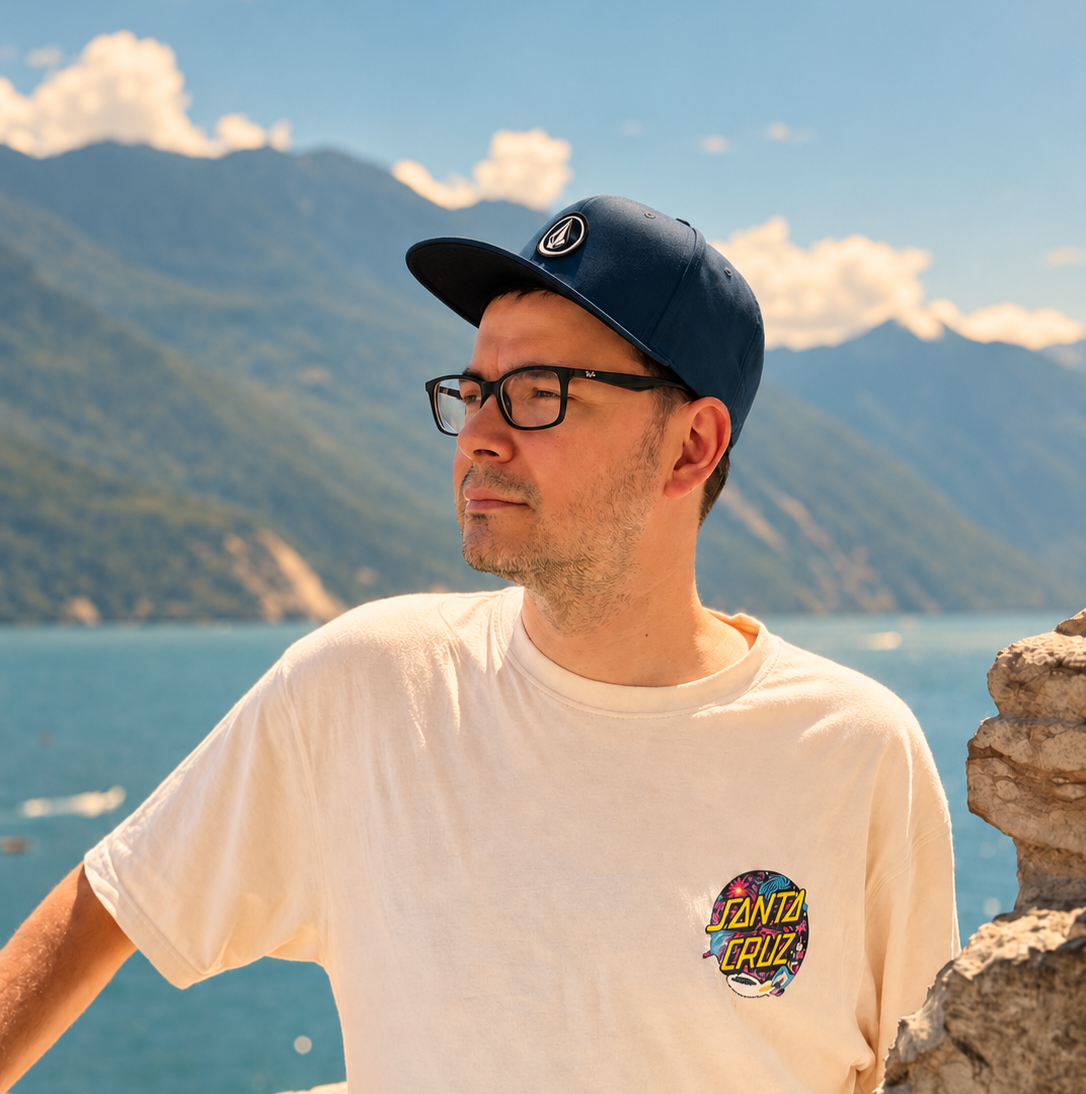
Hooked on security since 2001, back in school — mostly on how systems break. Over time that turned into building things: exploits, tools, my own SOAR, an AI security agent — systems that attack and defend on their own. I live in Berlin and write here about whatever I'm currently thinking through.
01
How things break, how to make breaking them cheaper for defenders, and how to build teams that do both.
02
Recent work first. Older tools and experiments are kept below.
An engine and agentic orchestration framework that plans, executes and iterates on security tests through tool-driven workflows, with people reviewing rather than driving each step.
AI assistants and rapid-prototyping habits for security analysis, automation, tooling and day-to-day operational orchestration.
An automated framework for the EU Cyber Resilience Act: requirements translated into controls, product-risk checks, evidence workflows and readiness tracking instead of spreadsheets.
Threat intelligence, hunting, detection engineering, triage and incident response wired into one closed loop that also drives risk prioritization.
Open-source, module-based framework for black-box CAN bus analysis and automotive security testing.
A native reverse DNS transport for Meterpreter, developed with Maxim Andreyanov.
An experimental honeypot that studied active responses to attackers targeting a public website.
03
Things I presented, newest first. Slides are kept here.
 2016Black Hat Europe, London
Black-box analysis of CAN networks and ECU devices with the open-source CANToolz framework: UDS scanning, traffic analysis, finding control frames and running MitM over the bus.
2013Black Hat Europe, AmsterdamAn experiment in active defense: a web honeypot that automatically counter-attacks everyone who tries to attack it, turning passive detection into automated response.
2012Black Hat Europe, AmsterdamPractical penetration of Lotus Domino infrastructure: from fingerprinting and service enumeration to vulnerability discovery and full compromise via the Domino console.
 2010Hack In The Box, Amsterdam
The first public PoC for JIT-Spray: bypassing DEP and ASLR in IE8, Firefox and Acrobat Reader via JIT-compiled ActionScript, with universal shellcode for Metasploit payloads.
04
I've been at HERE Technologies since 2013, moving between security research, product security, engineering and leadership. Today I'm Senior Director and Head of Security, responsible for a 40-person organization covering security operations, product security, platform security and security infrastructure.
Most of my time goes into making security an engineering discipline rather than a gate: security architecture and TARA under ISO/SAE 21434 inside the product lifecycle, vulnerability management and release decisions, a SOC that feeds risk prioritization — and, increasingly, AI doing the repetitive parts so people can do the interesting ones.
05
HERE since 2013 · Nokia before that · a decade of security research before that.
06
Disclosures, acknowledgements and publications, kept for the record.
The project "Honeypot that can bite" won the nomination "Best Project by an Approved DEF CON Group" — awarded by DEF CON at DEF CON 21, Las Vegas, 2013.
Vulnerabilities discovered during internal penetration testing and red team engagements and disclosed to vendors.
Listed by vendors and platforms for responsible vulnerability disclosure.
Contributed to the ROP and shellcoding section of the handbook.
ELSEWHERE